Summary
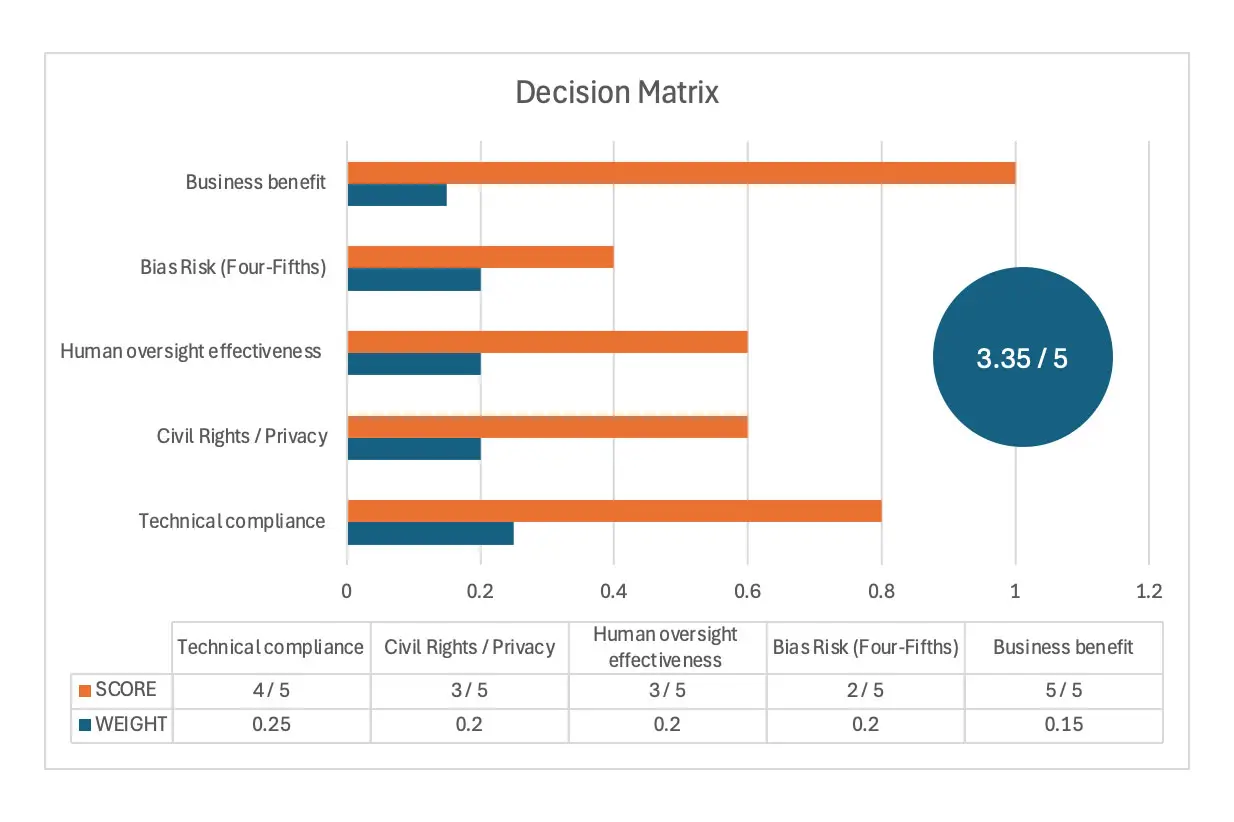
This risk assessment evaluates the Greenhouse ATS (Real Talent Sourcing & Match Tiering Suite). The report identifies the current state of the system alongside existing compliance and operational gaps, and provides remediation suggestions to address these vulnerabilities. It delivers a recommendation for deployment including mandatory operational stipulations and ongoing monitoring guidelines, offering a structured framework that can be applied to any business seeking to streamline their hiring process.
Federal and State Jurisdictional Triggers and Guidelines
NIST AI RMF, EEOC Title VII Guidance, NYC LL 144, California Cilvil Rights Act, Illinois AI Video/Zip Code Acts, Colorado AI Act
Key Findings
The system processes candidate’s personal data, reviews resumes through an integrated LLM API (OpenAI sub-processor), and groups applicants into categorized match tiers (Strong, Good, Partial, Limited). While Greenhouse prevents automatic system rejections, its sorting introduces distinct U.S. legal risks regarding automation bias through blind trust and proxy discrimination from historical hiring data.
Summary
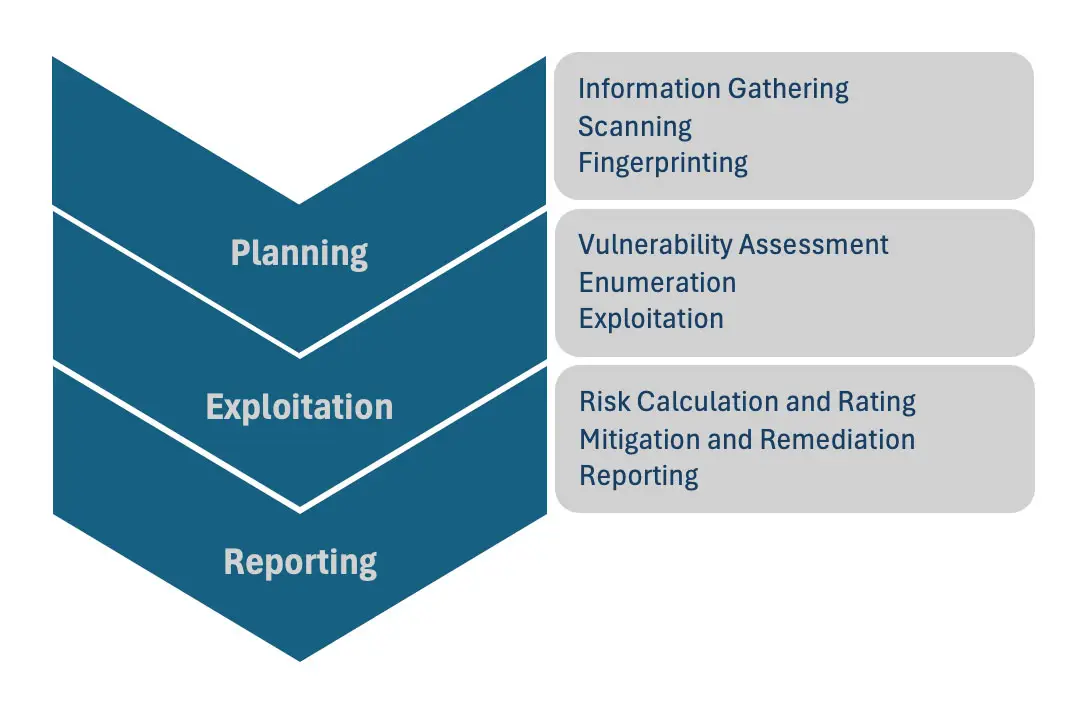
This internal grey-box security assessment details a simulated network penetration test executed against a fictional corporate environment. The lab infrastructure consisted of three virtual machines: one dedicated attacker computer and two vulnerable target systems configured with intentional security flaws and exposed services. The resulting deliverable includes an executive summary, testing methodology, detailed technical findings, and actionable remediation strategies.
Critical Findings
Unauthenticated Backdoor on Ubuntu Server
Security Utilities
Nmap, Metasploit, Kali Linux
Objective Achieved
Full target takeover and lateral movement
Key Takeaways
Network Vulnerability: Pivoting and lateral movement through a network via perimeter failure.
Gaps Identified: Deficiencies in log management, access control policies, and internal firewall rules.
Strategic Remediation: Enforced defense in depth and automated hardening.